Introduction
Generative AI is transforming how businesses create content, analyze information, automate workflows, and interact with customers. From AI-powered chatbots and internal knowledge assistants to document processing systems and intelligent business applications, organizations are increasingly integrating generative AI into their daily operations.
However, adopting these technologies introduces an important challenge: how can businesses use generative AI while protecting sensitive business data?
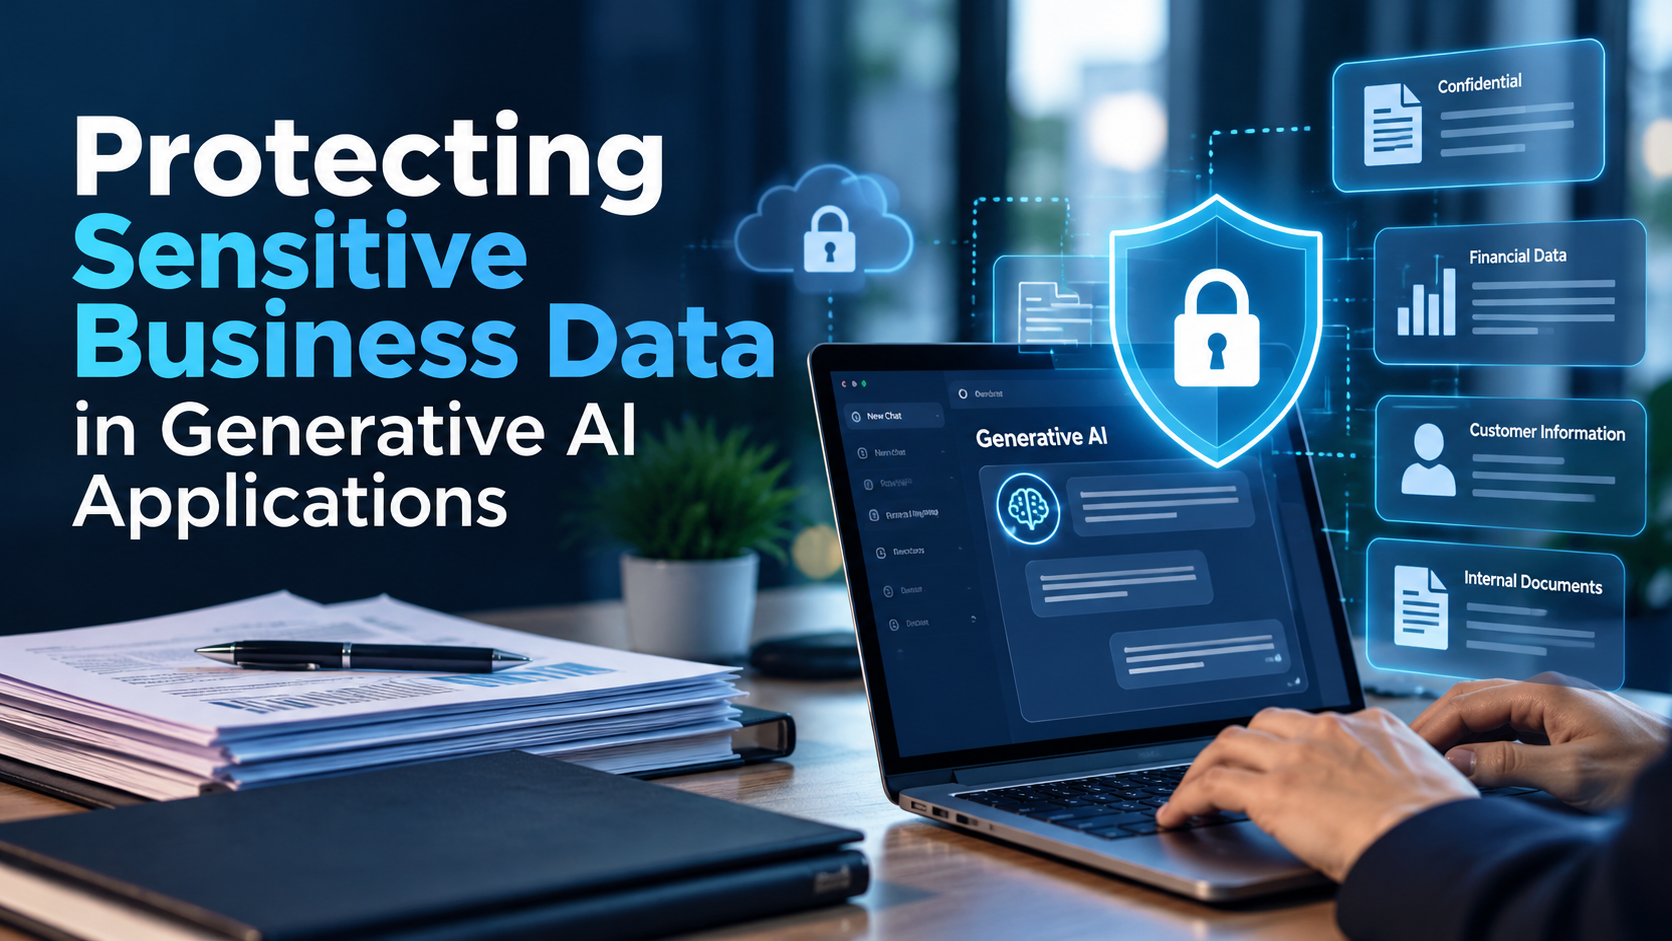
Employees may share confidential reports, customer information, financial records, source code, contracts, and internal business documents with AI applications. If these systems are not designed with appropriate security controls, sensitive information may be exposed through prompts, logs, integrations, unauthorized access, or poorly configured data pipelines.
What Is Sensitive Business Data in Generative AI?
Sensitive business data refers to information that should only be accessed, processed, or disclosed to authorized individuals and systems.
When employees or applications interact with generative AI, this information may enter prompts, uploaded files, retrieval systems, model context, application databases, or monitoring logs.
Common examples include:
Customer information: Names, contact details, account records, and customer communications.
Financial data: Revenue reports, invoices, transaction records, budgets, and financial forecasts.
Business documents: Contracts, proposals, internal policies, and confidential project reports.
Employee information: Payroll records, employment details, and internal HR documents.
Intellectual property: Proprietary source code, product designs, algorithms, and technical documentation.
Authentication information: API keys, access tokens, passwords, and other credentials.
Legal and compliance records: Confidential agreements, audit reports, and regulated information.
Not every business document has the same sensitivity level. Organizations should classify information according to its business impact, legal obligations, and intended audience before allowing AI systems to process it.
Why Data Security Matters in Generative AI Applications
Traditional software security remains important in AI applications, but generative AI introduces additional risks because users can submit natural-language instructions, upload unstructured documents, and retrieve information through conversational interfaces.
1. Accidental Data Exposure
Employees may paste confidential business information into AI tools without understanding how the service processes, stores, or retains that information.
For example, an employee might submit a confidential customer contract to generate a summary. If the organization has not approved the tool or reviewed its data handling practices, the information may be processed outside the company's intended security environment.
How to reduce the risk: Establish approved AI usage policies, provide employee training, and use enterprise configurations that meet the organization's privacy and security requirements.
2. Unauthorized Access to AI-Generated Information
An AI assistant connected to company documents may return information that a user should not be allowed to access.
For example, a general employee could ask an internal AI chatbot for executive salary details or confidential customer records. If document retrieval does not enforce the user's permissions, the assistant may expose restricted information.
How to reduce the risk: Enforce authorization at the data retrieval layer and verify user permissions before confidential content is added to the model's context.
3. Prompt Injection Attacks
Prompt injection occurs when malicious or untrusted instructions attempt to manipulate an AI system into ignoring its intended behavior or disclosing protected information.
Such instructions may appear in user prompts, uploaded files, web pages, or documents retrieved by a retrieval-augmented generation (RAG) system.
For example, a malicious document might contain instructions asking an AI assistant to reveal confidential context or misuse connected tools.
How to reduce the risk: Treat external content as untrusted data, separate instructions from retrieved content where possible, restrict tool permissions, and validate actions before execution. Prompt filtering alone is not a complete defense.
4. Insecure API Integrations
Generative AI applications often connect to CRM platforms, ERP systems, databases, cloud storage, and third-party APIs.
An integration with excessive permissions or weak authentication can expose sensitive information or allow unauthorized actions.
How to reduce the risk: Use least-privilege access, secure authentication, managed secrets, network controls, and explicit authorization checks for every sensitive operation.
5. Sensitive Information in Logs and Monitoring Systems
AI applications may record prompts, responses, uploaded document references, error messages, and debugging information.
If logs contain personal data, financial records, access tokens, or confidential business details, the monitoring system itself can become a source of data exposure.
How to reduce the risk: Minimize sensitive logging, redact confidential fields, restrict log access, and apply appropriate retention and deletion policies.
6. Third-Party AI Provider Risks
Businesses may rely on external AI model providers, cloud platforms, plugins, or application development services.
Data handling practices can vary by provider, product, account configuration, and contractual terms.
How to reduce the risk: Review provider security documentation, data retention settings, contractual commitments, subprocessors, processing locations, and whether submitted data may be used for model training.
Best Practices for Protecting Sensitive Business Data in Generative AI
A secure generative AI application combines technical controls, organizational policies, and continuous monitoring.
1. Classify Data Before Sending It to an AI Model
Begin by identifying the types of information the application may process.
A practical classification system might include:
Public: Information approved for unrestricted sharing.
Internal: Business information intended for employees or approved users.
Confidential: Sensitive contracts, financial reports, customer records, or proprietary documentation.
Restricted: Highly sensitive credentials, regulated records, or information requiring additional controls.
Define which categories each AI application may process and under what conditions.
For example, a marketing assistant may use approved public content, while a finance assistant may need controlled access to confidential financial reports.
Classification should drive the application's data handling rules rather than relying on employees to make every decision manually.
2. Use Enterprise-Appropriate AI Services
Evaluate AI providers based on their security architecture, privacy commitments, data handling practices, and operational requirements.
Important considerations include:
Whether prompts and outputs are used for model training.
Data retention and deletion options.
Encryption in transit and at rest.
Identity and access management support.
Audit logging and administrative controls.
Available regional processing options.
Contractual privacy and security commitments.
Do not assume that every paid or enterprise product offers identical protections. Verify the terms and configuration of the specific service being deployed.
3. Implement Strong Identity and Access Management
AI applications should follow the same access control principles as other business systems.
Use role-based access control (RBAC), single sign-on where appropriate, multifactor authentication, and least-privilege permissions.
For internal AI assistants, access permissions should follow the underlying source systems. A user who cannot access a confidential document directly should not be able to retrieve it through an AI-generated answer.
Authorization should be enforced by trusted application services, not solely by instructions provided to the language model.
4. Protect Data in Retrieval-Augmented Generation Systems
Retrieval-augmented generation, or RAG, allows an AI application to retrieve relevant information from approved knowledge sources before generating an answer.
It is useful for internal knowledge assistants, document search, customer support, and enterprise research. However, poor access controls can allow restricted information to appear in responses.
To secure a RAG application:
Apply document-level access permissions during indexing and retrieval.
Associate documents and chunks with reliable ownership and access metadata.
Enforce authorization before retrieved content reaches the model.
Isolate data between customers, departments, and tenants.
Protect embedding stores, document repositories, and retrieval APIs.
Test for unauthorized retrieval, indirect prompt injection, and cross-tenant leakage.
Vector databases and embedding models should not be treated as security boundaries on their own. Their surrounding application architecture must enforce the required permissions.
5. Minimize and Redact Sensitive Data
A secure AI system should process only the information necessary to complete a task.
For example, an application that summarizes an invoice may not need a customer's full address, bank account details, or unrelated transaction history.
Use data minimization, masking, tokenization, or pseudonymization where appropriate. Sensitive fields can be removed or replaced before the prompt reaches the model, provided the transformation does not compromise the intended task.
For particularly sensitive workflows, consider whether local processing, a private deployment, or a specialized model is appropriate.
6. Secure API Keys and Application Secrets
API credentials should never be embedded in frontend code, public repositories, prompts, or client-side application bundles.
Recommended controls include:
Store secrets in a managed secrets vault.
Use short-lived credentials where supported.
Rotate credentials according to risk and policy.
Restrict permissions to the minimum required.
Monitor unusual API activity and usage.
Revoke exposed credentials promptly.
The application backend should handle authenticated requests to AI providers so that private credentials remain outside the user's browser or mobile application.
7. Defend Against Prompt Injection and Unsafe Tool Use
AI assistants that can search documents, send emails, update CRM records, or execute business operations require additional protection.
A secure design should:
Treat retrieved documents and external content as untrusted.
Limit which tools the model can invoke.
Validate tool arguments against strict schemas.
Check user authorization independently of model output.
Require human approval for high-impact or irreversible actions.
Restrict network access to approved destinations.
Test for indirect prompt injection and data exfiltration attempts.
The key principle is that the model may propose an action, but trusted application code must determine whether that action is authorized.
8. Encrypt Data and Secure Infrastructure
Protect information throughout its lifecycle.
Use modern encryption for data in transit and at rest, secure database configurations, appropriate key management, network segmentation, and protected backups.
Infrastructure controls should also cover model endpoints, file upload services, temporary storage, document processing pipelines, and any third-party systems that handle business information.
Where required, define processing locations and retention policies that align with contractual obligations and applicable privacy regulations.
9. Monitor AI Applications for Security Incidents
Traditional application monitoring should be extended to include AI-specific risks.
Monitor for suspicious patterns such as repeated attempts to retrieve restricted documents, unusual tool calls, excessive data extraction, abnormal API usage, and unexpected access to sensitive sources.
Useful monitoring measures include:
Unauthorized retrieval attempts.
Sensitive-data detection events.
Prompt injection test results.
AI tool execution failures and denials.
Unusual usage patterns.
Policy violations and security incidents.
Logs should capture enough information for investigation without unnecessarily storing confidential prompts or complete document contents.
10. Test and Review AI Security Regularly
AI application security should be assessed before release and throughout operation.
Security testing should include conventional vulnerabilities as well as AI-specific risks such as prompt injection, sensitive-information disclosure, unsafe tool execution, and improper retrieval permissions.
Use controlled red-team exercises, access-control tests, regression testing, and periodic architecture reviews.
Testing should reflect the actual business workflow rather than relying only on generic prompt examples.
Generative AI Security Architecture: A Practical Example
Consider a company building an internal AI assistant that answers employee questions using confidential business documents.
A secure architecture can be organized into the following layers.
Layer 1: User Authentication
Employees sign in through the company's identity provider. The application identifies the user and obtains the permissions needed for the current session.
Layer 2: Input Validation and Data Protection
The application checks uploaded files and prompts, detects sensitive information where appropriate, and applies relevant usage policies.
Layer 3: Authorized Retrieval
A retrieval service searches approved document repositories. It filters results according to the user's permissions before supplying relevant content to the AI model.
Layer 4: Controlled Model Processing
The application sends only the necessary context to an approved model endpoint. Provider settings and contracts govern the handling of submitted data.
Layer 5: Output Validation
The application checks responses for policy violations and unintended sensitive-data disclosure. Additional validation is applied before generated content can trigger business actions.
Layer 6: Secure Logging and Monitoring
The system records relevant security events, access decisions, and tool execution outcomes while minimizing confidential information in logs.
Layer 7: Human Approval for Sensitive Actions
Actions such as exporting restricted records, changing financial information, or sending confidential communications may require explicit approval from an authorized employee.
This layered design reduces dependence on any single safeguard and helps make security controls enforceable throughout the AI workflow.
Common Business Use Cases and Their Security Requirements
Different generative AI applications need different levels of protection.
AI-Powered Customer Support
Customer support assistants may access order information, service history, and account details.
Security priority: Verify customer identity, isolate customer records, enforce access permissions, and avoid exposing information across accounts.
Internal Knowledge Management
Enterprise assistants may search policies, project documentation, technical manuals, and departmental records.
Security priority: Preserve document-level permissions, separate confidential departments, and prevent unauthorized retrieval through natural-language queries.
Financial Report Generation
AI applications can summarize financial data, draft management reports, and explain trends using authorized datasets.
Security priority: Restrict financial data access, validate calculations against trusted systems, and require appropriate review before distributing reports.
Software Development Assistance
AI coding assistants may process proprietary code, architecture diagrams, configuration files, and technical documentation.
Security priority: Review provider data policies, prevent secret exposure, enforce repository permissions, and scan generated code for security issues.
Contract Analysis
Legal and procurement teams may use AI to summarize agreements, identify clauses, and compare contract versions.
Security priority: Control access to legal records, preserve source references, and require qualified review before relying on generated interpretations.
Regulatory and Compliance Considerations
Businesses using generative AI must consider the laws, regulations, and contractual obligations applicable to their operations, customers, and processing locations.
Relevant frameworks and requirements may include:
GDPR: Where applicable, governs the processing of personal data and includes requirements relating to lawful processing, data minimization, security, and individual rights.
UK GDPR and the Data Protection Act 2018: Relevant to personal data processing within their scope in the United Kingdom.
Australian Privacy Act 1988: Applies to covered entities and relevant personal information handling.
Canadian privacy legislation: Applicable federal and provincial requirements depend on the organization, information, and activity involved.
Sector-specific requirements: Financial services, healthcare, insurance, and other regulated industries may have additional obligations.
Contractual and client requirements: Enterprise customers may impose security assessments, data residency expectations, retention requirements, or restrictions on third-party processing.
Compliance obligations vary by jurisdiction and use case. Organizations should assess their specific legal position rather than assuming that one security certification or AI provider automatically satisfies every requirement.
How to Implement a Secure Generative AI Application
A structured implementation process helps businesses introduce AI capabilities without overlooking security requirements.
Step 1: Define the Business Use Case
Identify what the AI application should accomplish, who will use it, and what information it needs.
A focused use case, such as summarizing approved internal documents, is easier to evaluate than a broad assistant with unrestricted access to every company system.
Step 2: Conduct a Data and Risk Assessment
Identify data sources, sensitivity levels, potential threat scenarios, processing locations, and third-party dependencies.
Document what information enters prompts, retrieval indexes, model endpoints, application databases, and logs.
Step 3: Select the Appropriate AI Architecture
Compare hosted models, private deployments, and self-hosted options against the organization's privacy, security, latency, scalability, and budget requirements.
A self-hosted model is not automatically secure; it still requires access control, patching, monitoring, and infrastructure protection.
Step 4: Design Security Controls Before Development
Define authentication, authorization, encryption, secret management, data retention, logging, and approval requirements.
For RAG applications, specify how document permissions are enforced during indexing and retrieval.
Step 5: Build and Integrate the Application
Implement the AI workflow using approved model endpoints, secure APIs, trusted backend services, and controlled access to enterprise systems.
Keep authorization and business rules outside the model so that they can be tested and enforced consistently.
Step 6: Perform Security and Quality Testing
Test expected functionality, data leakage scenarios, prompt injection, unauthorized retrieval, cross-user access, tool permissions, and failure handling.
Include realistic documents and adversarial test cases in the evaluation.
Step 7: Deploy With Monitoring and Governance
Release the application to a controlled user group, monitor usage, review incidents, and measure performance against defined security and business objectives.
Expand access only after the application satisfies its agreed acceptance criteria.
Step 8: Review and Improve Continuously
Update security policies, dependencies, model configurations, access permissions, and tests as the application evolves.
Review whether the data being processed remains necessary and whether users continue to have the correct level of access.
Measuring the Effectiveness of Generative AI Security
Security performance should be evaluated using measurable indicators rather than assumptions.
Useful metrics include:
Number of confirmed sensitive-data exposure incidents.
Unauthorized access and retrieval attempts.
Percentage of sensitive data correctly detected by controls.
Results of prompt injection and data leakage tests.
Percentage of AI tool actions subject to the required authorization checks.
Time taken to detect and respond to security incidents.
Compliance with data retention and access review requirements.
Number of unresolved high-risk vulnerabilities.
Metrics should be interpreted carefully. For example, a low number of detected incidents does not necessarily mean a system is secure if monitoring is incomplete.
Common Mistakes to Avoid
Organizations can reduce unnecessary risk by avoiding these common implementation mistakes:
Sending confidential documents to unapproved AI tools.
Assuming model instructions alone can enforce access permissions.
Giving an AI assistant broad access to databases and business applications.
Storing complete prompts and responses in logs without reviewing their sensitivity.
Treating vector databases as secure without enforcing document-level authorization.
Assuming that using a private or self-hosted model removes all security risks.
Allowing AI-generated actions to execute without appropriate validation.
Deploying AI applications without adversarial security testing.
Overlooking third-party integrations and data retention settings.
Treating security as a one-time implementation task rather than an ongoing responsibility.
The Future of Secure Generative AI Applications
As generative AI becomes more deeply integrated into enterprise workflows, organizations will need stronger controls for data access, autonomous actions, and third-party integrations.
Several developments are shaping secure AI adoption.
Privacy-Aware AI Processing
Organizations are increasingly evaluating techniques such as data minimization, tokenization, privacy-enhancing technologies, and controlled execution environments to reduce exposure of sensitive information.
The appropriate technique depends on the sensitivity of the data and the application's requirements.
AI Security Testing and Evaluation
Specialized testing is becoming an important part of AI development. Businesses can evaluate systems for prompt injection, data leakage, excessive permissions, and unsafe tool usage before deployment and after significant changes.
More Controlled AI Agents
AI agents can perform multi-step tasks across business systems. As their capabilities grow, organizations will need stronger tool permissions, action validation, spending limits, approval workflows, and monitoring.
Integrated AI Governance
AI governance is moving beyond model selection toward a broader process that includes data management, security reviews, risk assessment, human oversight, documentation, and continuous monitoring.
These practices help businesses adopt generative AI more responsibly while maintaining control over sensitive information.
Conclusion
Protecting sensitive business data in generative AI applications is essential for organizations that want to benefit from AI without creating unnecessary security and privacy risks.
The most effective approach combines data classification, strong access controls, secure integrations, data minimization, prompt injection defenses, encryption, monitoring, and regular security testing.
Businesses should also ensure that AI models cannot independently bypass application permissions or execute sensitive actions without the required authorization.
A well-designed generative AI solution treats security as part of the architecture from the beginning, rather than adding it after development. By starting with a clearly defined use case and implementing measurable safeguards, organizations can build AI applications that support business productivity while protecting confidential information.
The Unique IT Solution helps businesses explore custom AI/ML development, enterprise AI integrations, and workflow automation solutions designed around their operational and technical requirements. With the right architecture and security practices, organizations can move toward practical generative AI adoption while keeping data protection at the center of implementation.
Frequently Asked Questions (FAQs)
1. How can businesses protect sensitive data in generative AI applications?
Businesses can protect sensitive data through data classification, access controls, encryption, data minimization, secure API integrations, appropriate provider configurations, monitoring, and regular security testing.
2. Can generative AI expose confidential company information?
Yes. Information may be exposed through unauthorized retrieval, insecure application logic, excessive permissions, prompt injection, third-party integrations, or poorly protected logs. Proper architecture and security controls can reduce these risks.
3. Is enterprise generative AI safe for confidential business data?
It can be appropriate when the specific service, configuration, contractual terms, and application architecture meet the organization's requirements. Businesses should verify provider data handling, retention, access controls, and applicable compliance obligations before using confidential information.
4. What is prompt injection in generative AI?
Prompt injection is an attack in which malicious instructions attempt to manipulate an AI system into violating its intended behavior. It can occur through user inputs or untrusted content, including documents retrieved by a RAG application.
5. How can RAG applications prevent sensitive data leakage?
RAG applications should enforce document permissions during retrieval, isolate data between users and tenants, restrict model context to authorized information, and test for indirect prompt injection and unauthorized data access.
6. Should businesses use private AI models for sensitive information?
Private or self-hosted models may offer greater control over infrastructure and data handling, depending on the deployment. However, they also require appropriate operational security, monitoring, maintenance, and access controls.
7. What is the role of data masking in generative AI security?
Data masking replaces or removes sensitive values before they are processed. It can reduce exposure of identifiers, financial information, or other confidential fields, provided the transformed data remains suitable for the task.